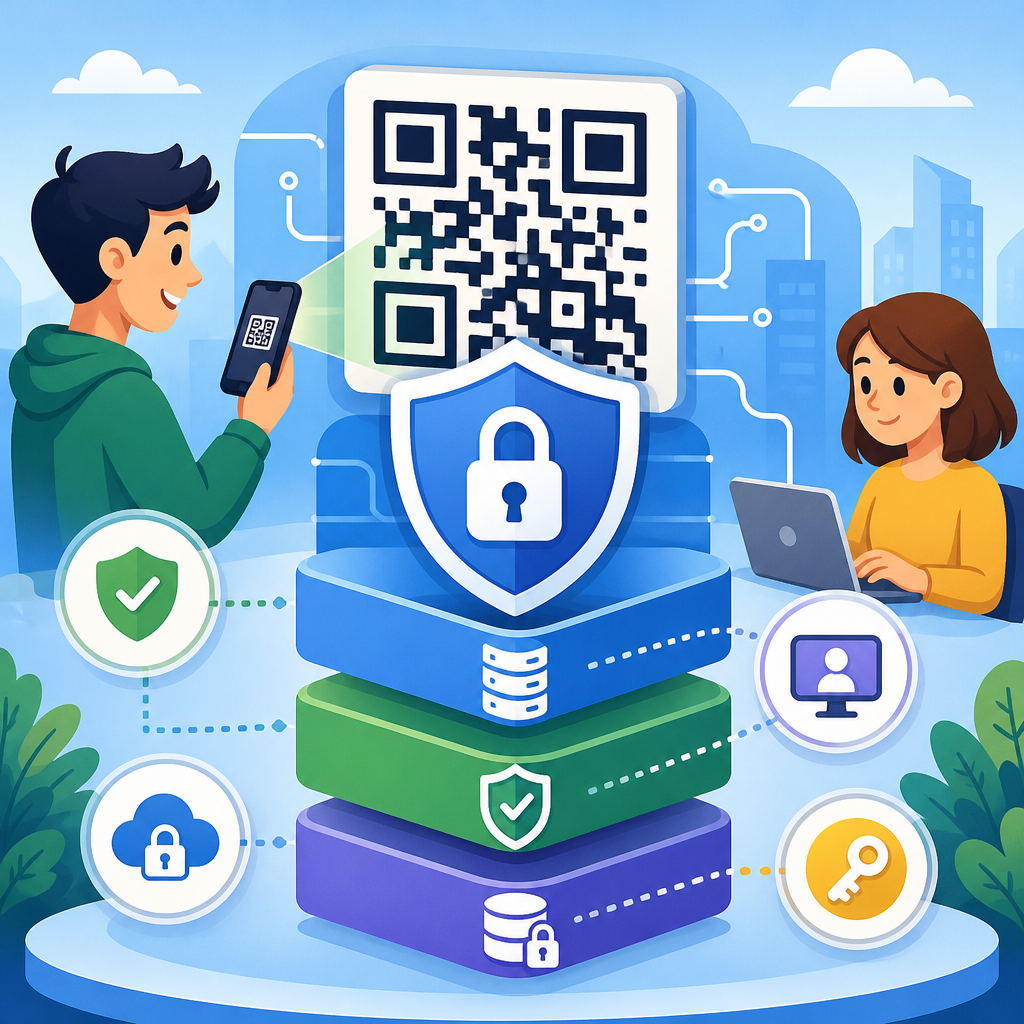
QR code system security architecture is the disciplined design of people, software, data flows, devices, and controls that keep QR-driven experiences safe from creation through scan, redirect, analytics, and retirement. In practice, building QR code systems means much more than generating a matrix image. A production-grade platform includes code generation services, short-link infrastructure, content management, campaign analytics, scanner interactions, access control, logging, and abuse prevention. When these parts are loosely assembled, attackers exploit the seams: malicious redirects, cloned codes, tampered print assets, poisoned analytics, credential theft, and privacy violations. When they are architected intentionally, QR systems become reliable channels for payments, ticketing, authentication, product traceability, restaurant ordering, and industrial workflows.
I have worked on QR deployments where the visible symbol was the smallest part of the engineering effort. The difficult work sat behind it: deciding whether codes should be static or dynamic, modeling redirect trust boundaries, limiting open-redirect abuse, protecting campaign dashboards, and ensuring scans from unmanaged mobile devices could not expose customer data. Security architecture matters because QR codes collapse the distance between physical and digital environments. A sticker on a window can trigger a browser session, deep link into an app, launch a payment request, or identify an asset on a factory floor. That convenience also expands the attack surface across printing vendors, content authors, mobile operating systems, APIs, and cloud infrastructure.
This hub article explains building QR code systems comprehensively, with security as the organizing principle. It defines the core building blocks, shows how to design trust boundaries, explains the risks that appear at each layer, and outlines the controls that experienced teams use in production. It also serves as a navigation center for deeper work on QR code generation, redirect platforms, analytics pipelines, authentication use cases, and anti-counterfeit implementations. If you are planning a marketing campaign, a digital menu platform, a warehouse labeling system, or a QR payment flow, the same architectural question applies: how do you make every scan trustworthy, observable, and resilient?
Core components of a secure QR code platform
A secure QR code platform starts with a clear component model. Most systems include a generator service, a storage layer for metadata, a redirect or resolution service, an administration interface, analytics collection, and integrations such as CRM, payment gateways, ticketing engines, or product databases. The QR image itself usually stores either a direct payload such as a URL, vCard, or Wi-Fi string, or a compact identifier that points to a managed endpoint. For enterprise systems, dynamic QR codes are usually preferred because they separate the printed symbol from the destination content. That allows updates, expiration policies, fraud review, and measurement without reprinting assets.
The generator service must create standards-compliant symbols with correct error correction levels and size parameters. ISO/IEC 18004 defines the QR Code symbology specification, and serious implementations follow it rather than relying on ad hoc rendering settings. Security begins even here. Teams should decide whether to encode raw destination URLs, signed tokens, opaque IDs, or encrypted references. Opaque IDs reduce data exposure, while signed tokens can prove integrity when codes are verified offline. The right choice depends on whether the scanner is online, whether destination content changes, and whether third parties can inspect or copy the symbol during distribution.
The redirect layer is the heart of many QR deployments. Instead of printing a final destination, the code points to a controlled domain that resolves the scan based on policy, device type, language, campaign state, inventory, or user authorization. This service must validate destinations against allowlists, normalize URLs, and prevent parameter injection. Open redirects are a common failure mode. If an attacker can create a QR that appears to use a trusted domain but forwards to malware, the brand’s credibility becomes the attacker’s delivery mechanism. Resolution services should also enforce HTTPS, HSTS, rate limiting, and signed administrative changes.
The administration interface deserves the same protection as a payment dashboard because it often controls live public links. In well-run systems, administrators authenticate with phishing-resistant multi-factor methods such as FIDO2 security keys, and authorization follows least privilege through role-based access control. A campaign editor may update copy but should not change domain settings or analytics retention. Every meaningful action should produce immutable audit logs. If a QR destination changes after a breach, investigators need to know who changed it, when, from which IP address, using which device, and through which API token or session.
Threat model and trust boundaries
The fastest way to improve QR code security architecture is to map trust boundaries before writing code. A typical scan journey crosses the physical environment, the user’s camera application, the mobile browser or app, public networks, CDN edges, application services, databases, and external integrations. Each hop changes what can be trusted. The printed code may be replaced. The scanning device may be unmanaged. The browser may suppress referrer data. A downstream partner may return unsafe content. When architects document those boundaries, controls become concrete instead of generic.
Common attack scenarios are predictable. Attackers place malicious stickers over legitimate QR codes in parking meters, restaurant tables, event posters, and product packaging. They clone authentic codes from websites and print them at scale for phishing. They exploit weak admin panels to swap destinations. They abuse analytics endpoints with bot scans that distort campaign reporting or trigger false inventory actions. They create denial-of-service conditions on redirect infrastructure during time-sensitive events such as ticketed entry. In industrial settings, they relabel assets so a maintenance worker scans a code and receives the wrong service procedure. Every scenario traces back to a trust boundary that was left unguarded.
A useful design pattern is to categorize scans by assurance level. Low-assurance scans are public marketing interactions where the destination is informational and no user data is required. Medium-assurance scans may personalize content or collect form submissions. High-assurance scans initiate payments, unlock physical access, authenticate a user, or retrieve regulated data. Security controls should scale with that assurance level. For example, a public brochure code can resolve to a cached landing page, while a payment or login code should use short expiration windows, signed requests, nonce validation, and device or session binding.
| Layer | Primary risk | Recommended control |
|---|---|---|
| Printed asset | Sticker replacement or cloning | Tamper-evident labels, visual verification marks, asset audits |
| Encoded payload | Data exposure or manipulation | Opaque IDs, signed tokens, minimal embedded data |
| Redirect service | Open redirect and malware delivery | Destination allowlists, URL canonicalization, HTTPS-only policies |
| Admin console | Account takeover | FIDO2 MFA, RBAC, session controls, audit logging |
| Analytics pipeline | Bot traffic and privacy leakage | Event validation, bot filtering, data minimization, retention limits |
| Integrations | Unsafe downstream content | Schema validation, API authentication, contract testing |
Data design, redirect logic, and cryptographic controls
Building QR code systems securely depends on conservative data design. Do not place secrets, personal data, or internal record identifiers directly in the code unless offline operation absolutely requires it. Anyone can photograph, forward, or archive a QR image. In most business systems, the safest pattern is an opaque identifier that resolves on the server. The identifier maps to metadata such as campaign, asset, locale, product SKU, or workflow state. This allows revocation, destination changes, and fraud review without exposing business logic in the symbol itself.
When integrity must be verified, use signed payloads. A common approach is to include a compact object containing an ID, expiration timestamp, intended action, and nonce, then sign it with HMAC-SHA-256 or an asymmetric scheme such as Ed25519 depending on the trust model. Symmetric HMAC is operationally simpler when one organization controls generation and verification. Asymmetric signatures work better when many verifiers need to trust issued codes without sharing a secret key. The signature does not hide the data, so encryption is still necessary if confidentiality matters. For regulated workflows, key rotation, secure secret storage, and signature versioning are mandatory.
Redirect logic should be deterministic and inspectable. I recommend a policy engine that evaluates destination rules in a fixed order: verify token status, check expiration, validate tenant ownership, confirm destination allowlist membership, apply locale or device overrides, and only then issue a redirect. Avoid free-form redirect parameters copied from incoming requests. If campaign managers need flexibility, store approved destination templates and limit which parameters may be substituted. This design sharply reduces injection risk and makes incident review easier because every redirect decision can be reproduced from logs.
Transport security is nonnegotiable. Every public endpoint should enforce TLS 1.2 or higher, redirect plain HTTP to HTTPS, and preload HSTS on primary domains where possible. If a mobile app scans codes and calls APIs directly, certificate pinning may be appropriate, although it adds operational complexity during certificate changes. Content Security Policy, secure cookies, SameSite attributes, and CSRF protections matter on landing pages and admin areas. These controls are not unique to QR systems, but QR platforms often underinvest in them because teams focus on symbol generation and overlook the web application that does the real work.
Operations, monitoring, and lifecycle governance
Security architecture succeeds or fails in operations. QR systems are long-lived: codes may stay on packaging, posters, machinery, menus, invoices, and manuals for months or years. That means governance must cover the full lifecycle from request and approval to generation, publishing, monitoring, change management, retirement, and archival. In mature programs, each code has an owner, business purpose, approved destination class, review date, and retention policy. Without that inventory, organizations accumulate orphaned redirects that nobody monitors but customers continue to scan.
Monitoring should combine availability, abuse detection, and business integrity checks. At the infrastructure layer, measure latency, error rate, DNS health, CDN cache performance, and origin saturation. At the application layer, alert on destination changes, failed admin logins, spikes in scans from unusual geographies, excessive user-agent diversity, and sudden increases in blocked redirects. At the business layer, watch for anomalies such as a product code resolving to the wrong region or a ticket validation code being scanned repeatedly in impossible time windows. Tools such as Datadog, Grafana, Cloudflare, and SIEM platforms like Splunk or Microsoft Sentinel make these patterns visible if event schemas are designed well.
Privacy governance deserves equal weight. QR analytics can collect timestamp, IP-derived location, device family, referrer context, and conversion events. That data is useful, but it can easily exceed what is necessary for the stated purpose. Good architecture applies data minimization: store the least data required, aggregate when possible, set retention windows, honor consent requirements, and separate analytics from identity unless the use case clearly requires linkage. For operations in the European Union, teams must align processing with GDPR principles. In California, CCPA and CPRA obligations affect disclosure, access, and deletion practices. The safest habit is to design analytics as a governed subsystem, not a marketing afterthought.
Finally, resilience planning should assume compromise attempts and operational mistakes. Keep tested backups of metadata, templates, and audit logs. Use infrastructure as code so redirect services can be rebuilt consistently. Stage changes behind approvals for high-assurance codes. Run tabletop exercises for domain hijack, admin account takeover, malicious destination swap, and partner API outage. Document scanner fallback behavior when a destination is unavailable. A QR code system feels simple to the end user because the architecture absorbs complexity. Building that reliability is the real engineering task, and it is the foundation for every deeper article in the QR Code Technology & Development hub. Use this hub as your blueprint, then audit your own QR estate, classify assurance levels, and prioritize the highest-risk flows first.
Frequently Asked Questions
1. What is QR code system security architecture, and why does it matter?
QR code system security architecture is the end-to-end design framework that protects every component involved in a QR-driven experience, not just the image itself. A secure architecture covers how QR codes are created, how they map to URLs or actions, how redirects are handled, how scanners and mobile devices interact with destination content, how analytics are collected, and how the entire lifecycle is governed from launch to retirement. In a production environment, QR campaigns rely on multiple moving parts, including generation services, short-link infrastructure, campaign management tools, content hosting, access permissions, telemetry, and fraud controls. Each layer introduces potential risk if it is not intentionally designed and monitored.
This matters because QR systems often connect physical environments to digital services in ways users trust instinctively. A customer scanning a code on packaging, signage, invoices, event badges, or product labels usually expects a safe and seamless interaction. Attackers exploit that trust through code tampering, malicious redirects, fake landing pages, unauthorized destination changes, data leakage, or abuse of analytics and tracking systems. Without a disciplined security architecture, organizations can expose users to phishing, malware distribution, credential theft, privacy violations, and brand damage. Strong architecture reduces those risks by defining trusted workflows, limiting who can change destinations, validating inputs, securing redirects, hardening infrastructure, and creating clear visibility into suspicious behavior.
In short, QR code system security architecture matters because the QR code is only the visible entry point. The real security challenge lives in the systems behind it. Organizations that treat QR as a simple graphic asset usually miss the operational, technical, and governance controls required to keep the entire experience safe at scale.
2. What are the biggest security risks in a QR code platform?
The biggest risks typically fall into several categories: destination abuse, infrastructure compromise, user deception, data exposure, and operational mismanagement. One of the most common threats is malicious redirection. If an attacker gains the ability to alter destination URLs, they can silently send users to phishing pages, malware downloads, counterfeit storefronts, or fake login portals. This is especially dangerous in dynamic QR systems, where the visible code remains unchanged but the backend destination can be edited. Strong change controls, approval workflows, audit logging, and URL validation are essential defenses against this type of abuse.
Another major risk is the compromise of the short-link and redirect layer. Many QR systems depend on shortened URLs or redirect services to enable campaign updates, device routing, localization, analytics, and A/B testing. If that redirect infrastructure is insecure, it becomes a high-value target. Weak authentication, insecure APIs, poor key management, inadequate rate limiting, or vulnerable admin panels can give attackers control over large numbers of active QR codes at once. Similarly, poorly secured content management systems can allow unauthorized edits to campaigns, destinations, metadata, or embedded tracking rules.
User-facing attacks are also significant. Attackers may place fraudulent QR stickers over legitimate codes, distribute fake codes in emails or printed materials, or mimic a trusted brand’s design to encourage unsafe scans. Even if the platform itself is well built, users can still be tricked into interacting with malicious copies outside the official system. This is why platform security should be complemented by brand verification practices, tamper-evident physical deployment methods, and clear destination transparency for users.
Data privacy is another critical area. QR platforms often collect scan location, device type, timestamps, referral data, campaign attribution, and behavioral analytics. If this data is over-collected, stored insecurely, shared too broadly, or retained too long, the platform can create compliance and privacy risks. Finally, operational gaps such as missing monitoring, lack of incident response playbooks, poor decommissioning processes, and excessive admin privileges can turn small issues into major breaches. The strongest platforms assume risk exists across the full lifecycle and build controls accordingly.
3. How should a secure QR code system be designed from generation through redirect and analytics?
A secure QR code system should be designed as a controlled lifecycle, where each stage has distinct safeguards. At the generation stage, the platform should create codes through authenticated services with role-based access control, strong input validation, and policy enforcement around what types of destinations are allowed. If dynamic QR codes are supported, there should be governance over who can create them, who can edit them, and whether destination changes require review or dual approval. The code record should be tied to immutable identifiers, timestamps, ownership metadata, and full audit history so that every action is attributable.
At the redirect stage, the system should use hardened short-link infrastructure with TLS everywhere, secure DNS practices, WAF protection where appropriate, request validation, rate limiting, bot filtering, and strict backend authorization for any destination changes. Redirect logic should be carefully constrained. For example, destination domains can be allowlisted, unsafe protocols can be blocked, and suspicious query parameter injection can be rejected. Redirects should also be observable, meaning security teams can track unusual spikes, geographic anomalies, repeated scanner abuse, or patterns that suggest automated exploitation or campaign hijacking.
Analytics should be designed with both utility and privacy in mind. A secure architecture collects only the data that supports legitimate business needs and protects it with encryption, access controls, retention limits, and segmentation. Reporting interfaces should be permissioned so users only see campaigns and metrics relevant to their role. Sensitive event logs should be tamper-resistant and integrated into centralized monitoring systems for alerting and forensic review. If third-party analytics or marketing platforms are involved, those integrations should be reviewed for token security, data minimization, and contractual compliance obligations.
Across the full system, secure design principles should include least privilege, segregation of duties, environment isolation, secret management, vulnerability management, and documented retirement workflows. When a campaign ends, the organization should know whether the code should continue redirecting, display an informational landing page, or be disabled completely. A mature architecture treats generation, redirect, analytics, and retirement as one continuous security problem rather than separate features.
4. What controls help prevent QR code abuse, tampering, and unauthorized changes?
The most effective controls combine technical safeguards, administrative governance, and physical protections. On the technical side, role-based access control is foundational. Not every user should be able to generate, edit, publish, or retire QR destinations. High-risk actions, such as changing a live destination or exporting analytics, should require stronger permissions and ideally multi-factor authentication. Many organizations also benefit from approval workflows, where one person proposes a change and another authorizes it. This reduces the risk of insider abuse, account compromise, and accidental misconfiguration.
Comprehensive logging is equally important. Every meaningful event should be recorded, including code creation, edits, redirects, authentication attempts, permission changes, API access, and content publication. Those logs should be centralized, monitored, and retained according to policy so teams can investigate suspicious activity quickly. Domain allowlisting is another powerful control. If a QR platform only permits redirects to approved domains or vetted destination patterns, attackers have far fewer opportunities to turn a legitimate code into a phishing vector. Input validation, malware scanning for hosted assets, API authentication, rate limiting, and anomaly detection all add additional resilience.
For abuse prevention, organizations should watch for unusual scan behavior such as sudden traffic spikes, impossible geographic distributions, repetitive user-agent patterns, and redirect chains that do not match expected campaign behavior. These can indicate bot activity, scraping, fraud, or compromised assets. On the physical side, tamper-evident labels, secure placement, routine inspections, and print governance can reduce the risk of sticker overlays or unauthorized replacements in public spaces. Some deployments also include branded landing pages and visible trust signals so users can recognize legitimate destinations more easily.
Finally, change management and asset inventory are often overlooked but essential. Security teams should know which QR codes exist, where they are deployed, what they point to, who owns them, and when they expire. Unauthorized changes are much easier to detect when there is a current inventory, a defined owner for every asset, and clear retirement procedures for old or abandoned campaigns.
5. How do organizations balance security, privacy, and usability in QR-driven experiences?
Balancing security, privacy, and usability starts with recognizing that all three are part of trust. A QR experience that is highly secure but confusing to users will fail in practice, while a frictionless experience with weak controls can expose both users and the business to serious harm. The best approach is to apply security measures that meaningfully reduce risk without creating unnecessary complexity. For example, organizations can secure redirects, validate destinations, and monitor abuse behind the scenes while still delivering fast mobile-friendly landing pages and simple scan flows. Users should not have to become security experts to interact safely with a QR code.
Privacy should be addressed through intentional data governance. That means collecting only the analytics needed for business and operational purposes, being transparent about what is gathered, limiting retention, and restricting internal access. If location, device, or behavioral data is collected, the organization should have a lawful basis, clear disclosures where required, and controls that prevent analytics from becoming uncontrolled surveillance. Privacy-by-design practices make the platform more defensible and often simplify compliance with internal policy and external regulations.
Usability can be improved by making destinations recognizable and trustworthy. Clear branding, HTTPS, concise preview domains, understandable landing pages, and consistent campaign behavior all help users feel confident. Internally, usability